The IoT Security Foundation (IoTSF), in partnership with SafeShark, brought together cybersecurity specialists, industry experts and product manufacturers in London on Thursday 8th October 2026 for ‘You’re STILL not ready for the CRA’, a full-day event exploring the practical challenges of preparing for the EU Cyber Resilience Act (CRA).
Following the success of the Foundation’s first CRA-focused event in July 2026, this second gathering moved beyond regulatory awareness to examine what compliance means in practice, from reporting obligations and emerging standards to product classification, risk assessment, vulnerability management and secure product design.
With the CRA’s vulnerability and incident reporting obligations having taken effect on 11th September 2026, and the wider requirements becoming applicable on 11th December 2027, the event delivered a clear message: Cyber resilience is no longer simply a technical consideration, but an ongoing business responsibility requiring action across the entire product lifecycle.
From regulation to real-world implementation
Opening the event, Alex Buchan of SafeShark set the scene for a day of practical discussions examining how manufacturers and technology providers can translate the CRA’s requirements into effective security processes.
A central focus was Article 14, which introduces reporting obligations for actively exploited vulnerabilities and severe security incidents. Richard Marshall of Xitex, who chairs the relevant CENELEC and BSI standards working groups, joined Joe Lomako of TÜV SÜD for a fireside chat exploring the implications of the reporting requirements.
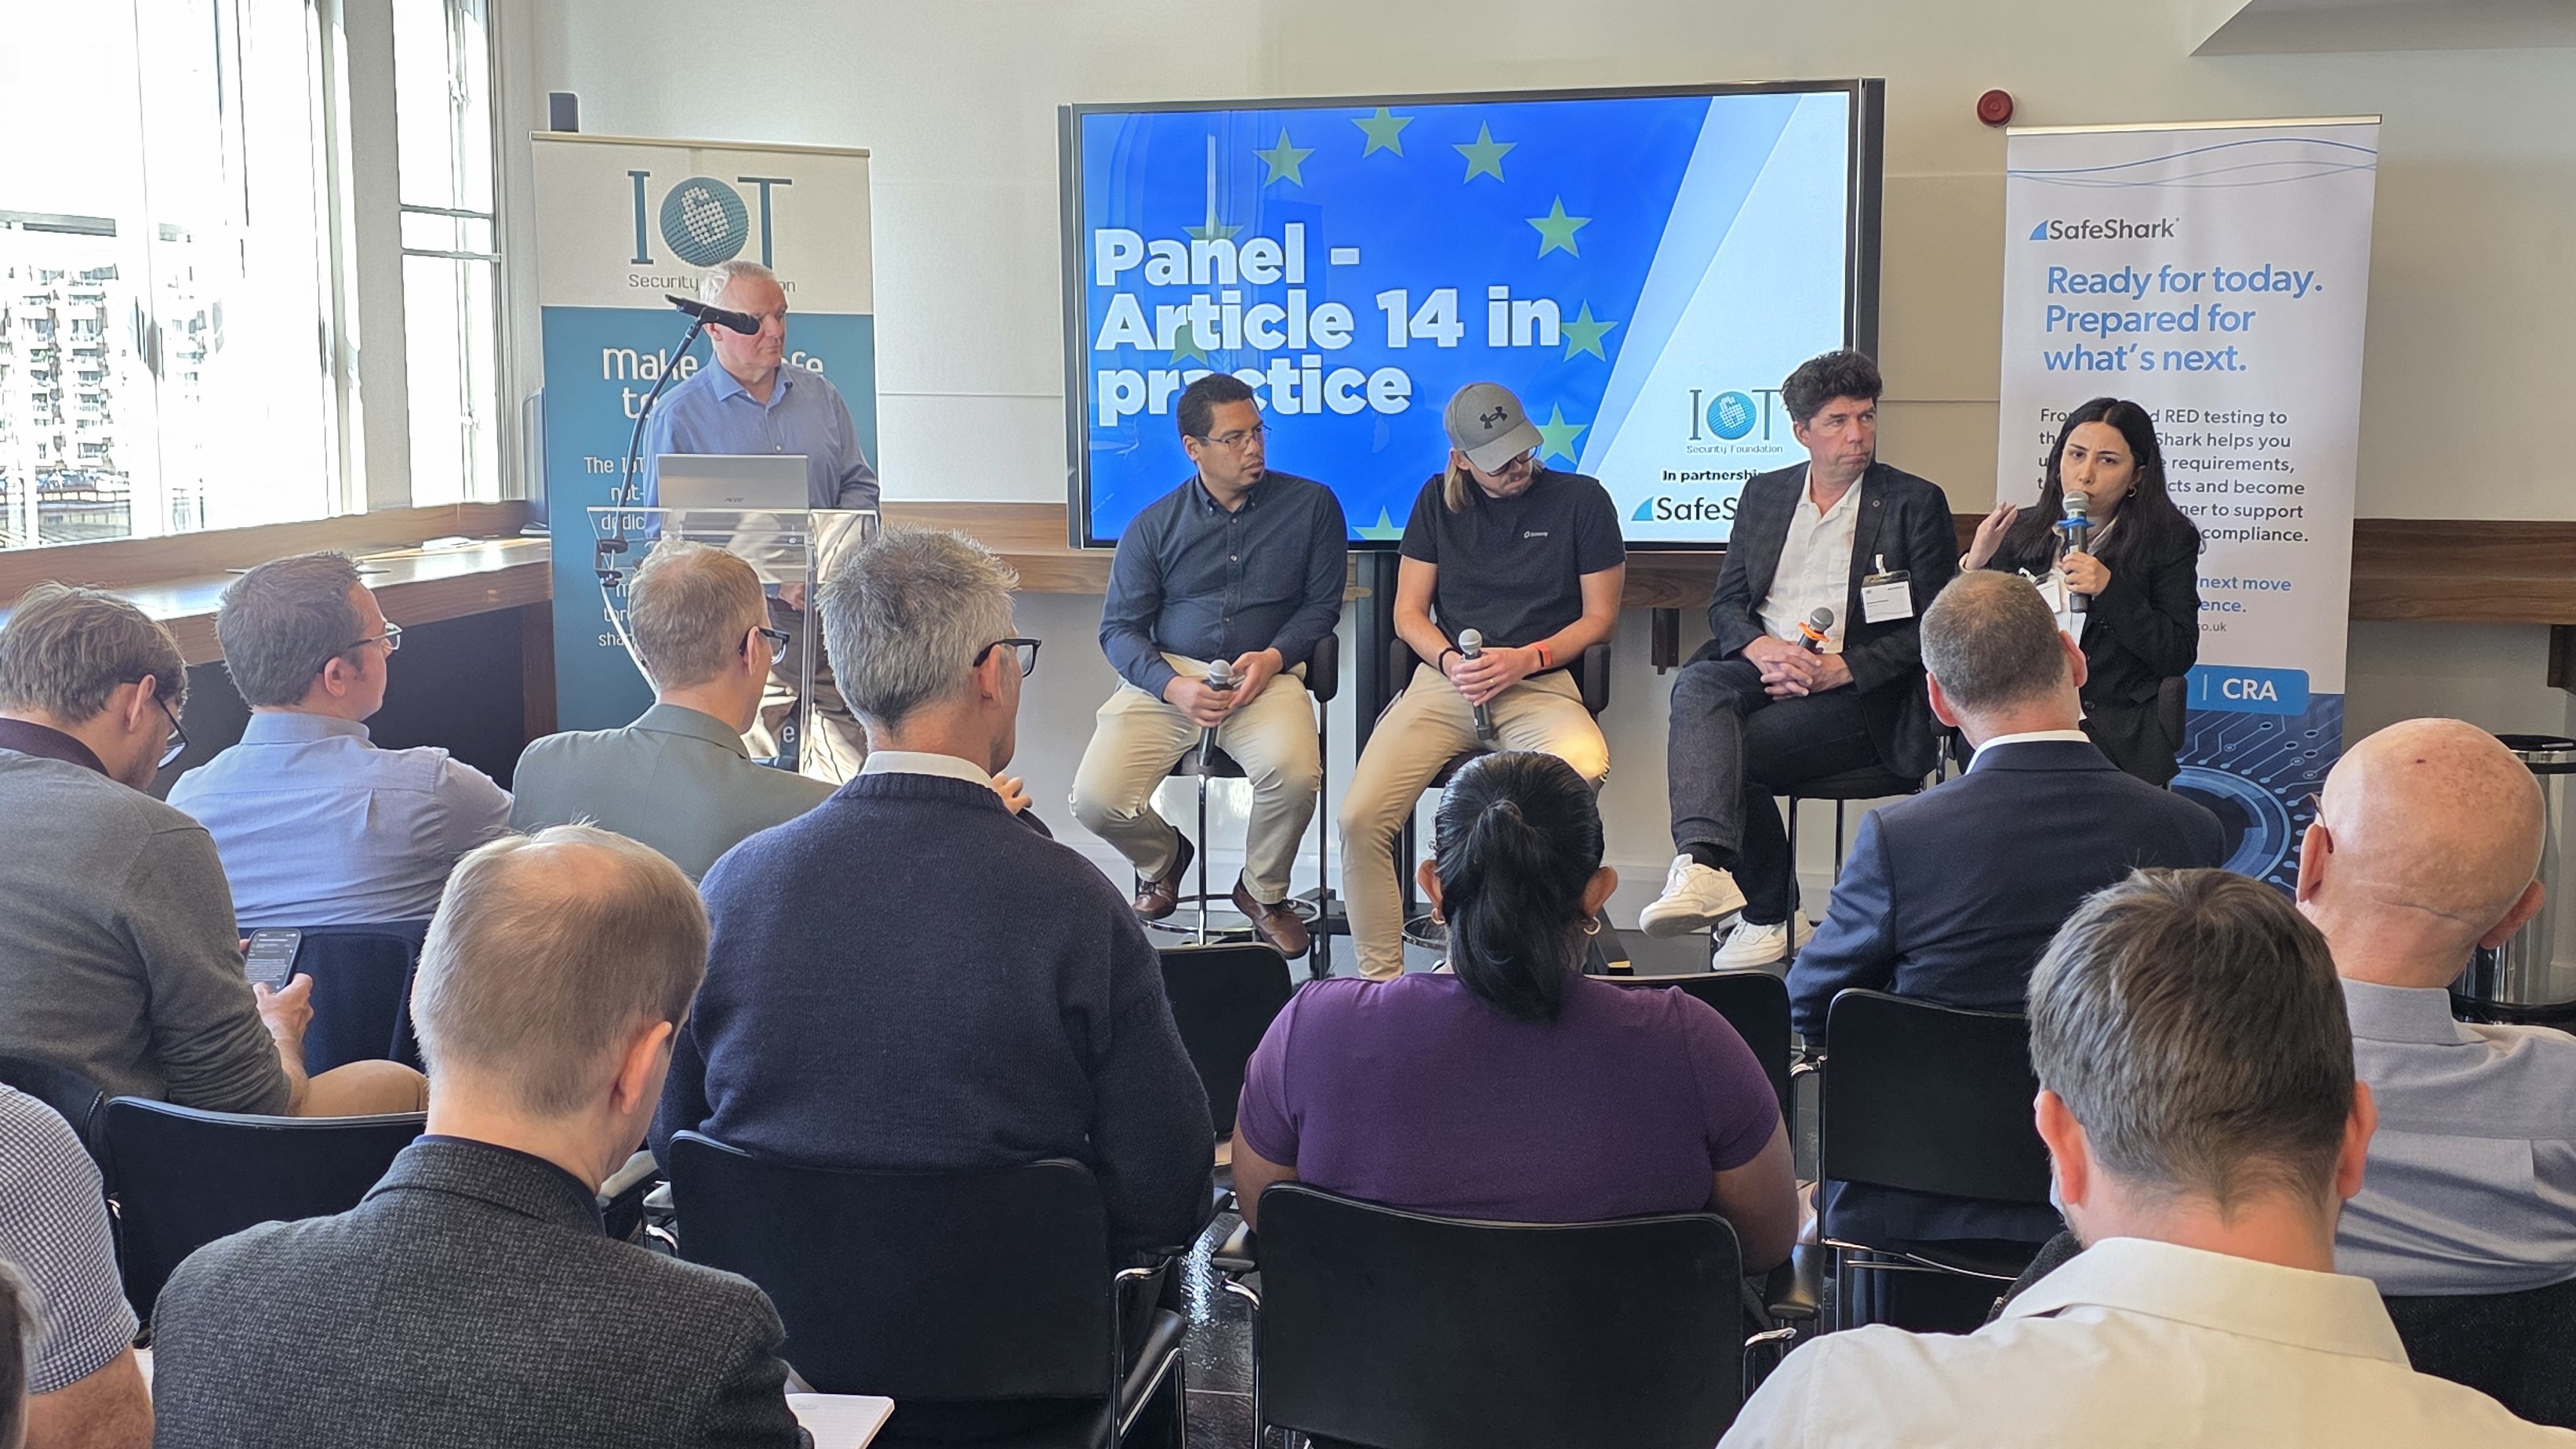
A subsequent panel brought together Richard Marshall, Mustanir Ali of Element, Viktor Petersson of Screenly, Jonathan Marshall of SafeShark and Zahra Khani of Keysight to consider the practicalities of meeting these obligations.
The discussions highlighted the importance of establishing effective vulnerability identification, escalation and reporting processes, ensuring that manufacturers have the necessary procedures in place before an incident occurs.
Understanding the standards and compliance requirements
The development of harmonised European standards was another major theme of the event.
Richard Marshall provided an update on the emerging EN 40000 series of standards, which will support manufacturers in demonstrating conformity with the CRA’s essential cybersecurity requirements.
These include principles for cyber resilience, vulnerability handling and generic security requirements, alongside product-specific standards being developed through ETSI.
With several standards still progressing through the approval process, the session provided valuable insight into the evolving regulatory landscape and the technical requirements manufacturers should be anticipating.
Paul Phillips of Resideo examined the broader implications of Article 13, particularly the responsibilities placed on manufacturers to demonstrate security by design, maintain technical documentation, manage vulnerabilities and provide security support throughout a product’s expected lifetime.
His presentation reinforced that CRA compliance extends beyond the initial product release. Manufacturers must consider their software development lifecycle, component suppliers, vulnerability management capabilities and long-term support arrangements.
Real-world testing reveals common security weaknesses
One of the day’s most practical sessions came from Jonathan Marshall, Co-founder and Director of SafeShark, who shared findings from the company’s extensive product security testing experience.
Drawing on hundreds of tests carried out against consumer IoT devices under the UK’s Product Security and Telecommunications Infrastructure (PSTI) requirements, the Radio Equipment Directive (RED) and early CRA assessments, the presentation identified recurring weaknesses that continue to create compliance challenges.
These included outdated software components with known vulnerabilities, inadequate documentation, poorly managed cryptographic keys, unnecessary network services and insufficient vulnerability disclosure procedures.
The testing evidence also demonstrated how seemingly straightforward security issues can become significant obstacles to market access.
For example, SafeShark’s data indicated that resolving certain cryptographic key management failures took an average of approximately 99 days, illustrating the potential impact of addressing security weaknesses late in product development.
The session emphasised three practical approaches: Reducing unnecessary attack surfaces, ensuring network interfaces and services are properly documented and secured, and implementing robust encryption, including for communications over local networks.
The wider lesson was that manufacturers should build security into products from the outset rather than relying on testing and remediation immediately before launch.
Product classification, risk assessment and threat modelling
The afternoon programme explored how manufacturers can determine the appropriate conformity assessment route for their products.
Mustanir Ali, Head of Cyber Product Assurance at Element, explained the CRA’s product classification system, including default, important and critical product categories, and how these classifications influence assessment requirements.
The session highlighted the importance of understanding a product’s core functionality, identifying applicable standards and establishing what technical evidence will be required to demonstrate compliance.
Risk assessment and threat modelling were also examined in detail.
Jonny Tyers of Threatplane explored the role of structured threat modelling in identifying security risks, understanding attack surfaces and connecting technical architecture with compliance evidence.
The presentations demonstrated how a risk-based approach can help organisations prioritise remediation, strengthen security architecture and maintain an evidence-based understanding of product cybersecurity throughout development and deployment.
Vulnerability management is a continuing obligation
David Pashley of Direct Insight, representing the IoTSF Regulatory Watch Working Group, examined the CRA’s vulnerability handling requirements and the emerging EN 40000-1-3 standard.
His presentation drew an important distinction between having a coordinated vulnerability disclosure policy and operating a comprehensive vulnerability handling process.
Manufacturers must be able to identify, monitor, assess and address vulnerabilities throughout the support period, including those affecting third-party software and hardware components.
Software Bills of Materials (SBoMs), active vulnerability monitoring, secure software updates and supplier due diligence were identified as essential elements of effective product security management.
The session also reinforced that manufacturers cannot simply transfer responsibility for vulnerabilities to upstream suppliers or open-source software providers. Accountability for the security of the finished product remains a fundamental consideration.
Secure boot and building trust into connected products
The day’s technical programme concluded with an introduction to secure boot from Ian Pearson of Microchip, drawing on work undertaken by the IoTSF Assurance Framework Working Group.
The presentation explored how secure boot establishes a root of trust within a device, allowing the integrity and authenticity of software to be verified during the startup process.
Through practical examples, the session demonstrated how weaknesses in device authentication, software integrity and update mechanisms can undermine otherwise secure systems.
It also emphasised that secure boot is not a complete security solution in isolation. Effective protection depends on combining trusted boot mechanisms with secure development practices, appropriate cryptographic controls and robust software supply chain security.
The message to industry: Start preparing now
Across the day’s presentations and discussions, a consistent theme emerged: CRA readiness cannot be achieved through a last-minute compliance exercise.
The regulation requires manufacturers to establish sustainable cybersecurity processes encompassing product design, development, testing, documentation, vulnerability monitoring, incident reporting and long-term security support.
The experiences shared by speakers also demonstrated that many of the most significant challenges are organisational rather than purely technical.
All slides are available via our members’ platform, go to Plenary> Docs & Files> You’re STILL not ready for the CRA
Video recordings will be drip-fed on our YouTube channel.