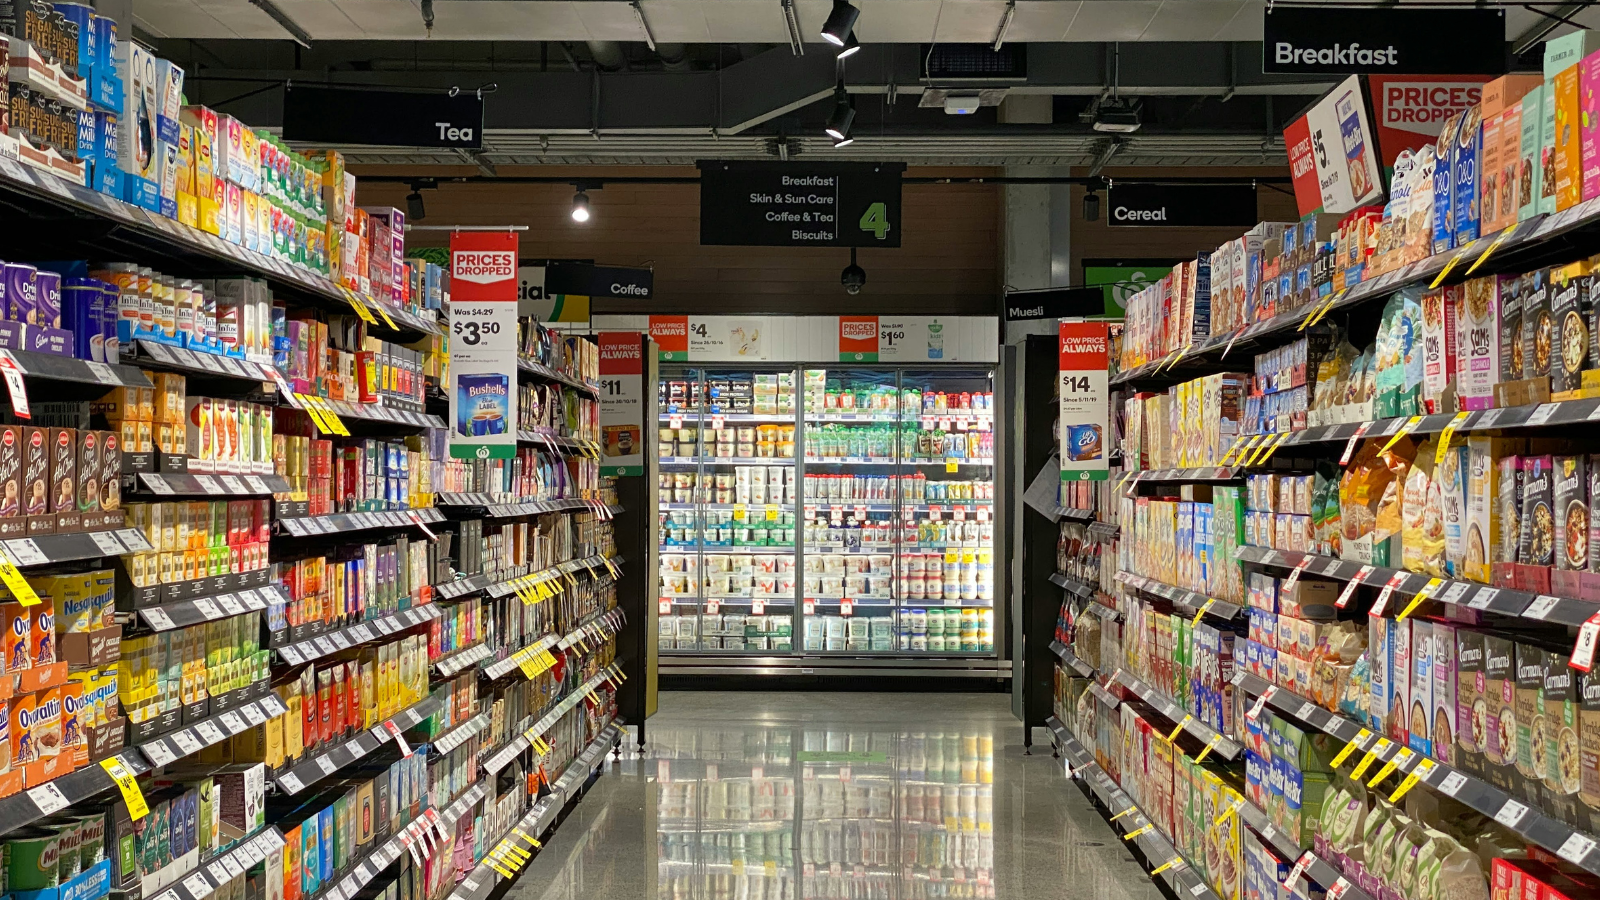
Recent cyberattacks targeting supermarket refrigeration systems across Europe have highlighted a growing and often overlooked cybersecurity risk: The vulnerability of connected operational equipment.
From refrigeration controllers and remote monitoring systems to wider building management infrastructure, increasingly connected environments are creating new opportunities for cyber criminals to disrupt business operations. But could stronger cybersecurity requirements, and the introduction of the EU Cyber Resilience Act (CRA), have helped prevent these incidents?
Tomorrow, Tuesday 17th November, the IoT Security Foundation (IoTSF) will bring together experienced industry experts for a special webinar exploring the cybersecurity implications of these attacks, the lessons organisations should take away, and what needs to change to better protect connected systems.
What will the webinar cover?
The session will begin with an opening presentation from Viktor Petersson (Screenly), who will explore the issues surrounding the recent attacks on supermarket refrigeration infrastructure and the wider implications for connected products and operational technology.
The presentation will set the scene for a discussion about the security weaknesses that can exist in connected equipment, the potential consequences for businesses, and whether existing cybersecurity practices and regulatory requirements are sufficient to address these risks.
An expert panel discussion
Following Viktor’s presentation, we will move into a panel discussion featuring:
Viktor Petersson (Screenly)
Michael Richardson (Sandelman)
Ken Munro (Pen Test Partners)
Bringing together expertise in secure product development, IoT cybersecurity and hands-on penetration testing, the panel will examine the issues from different industry perspectives.
Among the questions we expect to explore are:
What do recent attacks on supermarket refrigeration systems tell us about the security of connected operational equipment?
How exposed are businesses to attacks targeting systems outside their traditional IT infrastructure?
Could the Cyber Resilience Act have helped prevent these incidents, and what difference will it make in practice?
Where does responsibility for securing connected equipment sit between manufacturers, suppliers, installers, maintenance providers and end users?
What practical steps should organisations take now to reduce their exposure?
The discussion will also consider the importance of building security into products from the outset and maintaining appropriate cybersecurity protections throughout their operational lifetimes.
Why should you attend?
Cybersecurity is no longer simply an IT issue. As businesses become increasingly dependent on connected equipment and remotely managed infrastructure, vulnerabilities in operational technology can have very real consequences for business continuity, safety and financial resilience.
The recent refrigeration attacks provide a timely reminder that even equipment traditionally regarded as operational infrastructure can become a target.
For manufacturers, technology providers, retailers, system integrators and cybersecurity professionals, this webinar offers an opportunity to hear from experienced practitioners, explore the implications of the evolving regulatory landscape and gain a better understanding of the practical measures needed to secure connected environments.
Join us tomorrow
The webinar takes place on Tuesday 17th November 2026.
Registration is open and attendance is free.
We look forward to welcoming you.